
Prevent errors
with compliance engineering.
Product safety, information security & verifiable proof for authorities, customers, and auditors
“Policies do not pass audits. Active processes and robust, verifiable evidence do.”
Michael Kirsch Cyber Security · Lead Auditor · TISAX® Trainer
 AI-generated
Without proof of cyber security, type approval for new vehicles has been unavailable since July 2024, CE marking for connected products will no longer be possible from December 2027, and supplier clearance from most OEMs is already denied today. The Cyber Resilience Act, UN R155, NIS2, TISAX®, and ISO/IEC 27001 impose distinct requirements on products and organizations. They all share one common reality: merely understanding and implementing them is insufficient; the evidence must withstand scrutiny from authorities, customers, and auditors.
We combine compliance engineering with an auditor’s perspective, translating regulatory, normative, and customer-specific requirements into measures that perform effectively in day-to-day operations.
What we stand for.
CRA & Product Cybersecurity
Expert Opinions & Assessments
CRA & Product Cybersecurity
We identify interdependencies across the entire product lifecycle — from initial concept to recall. Not isolated cases, but always the entire system.
Learn more
Training Courses
CRA & Product Cybersecurity
We offer a broad portfolio of training courses. The primary focus is meeting legal and regulatory requirements for companies and technical products. All training courses were developed by our team…
Learn more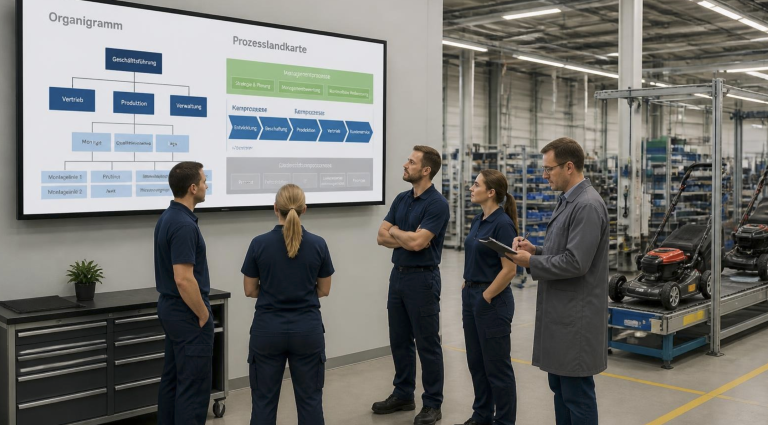
Management Systems
CRA & Product Cybersecurity
Our team of legal experts and engineers possesses a strong dedication to structure and order. We are, of course, ISO 9001 certified — without bureaucratic paperwork or dead-end documentation. We channel our passion…
Learn moreBetween regulation and technology.
We combine technical depth with legal precision. Our clients seek certainty — we deliver structure. We do not think in mere paragraphs, but in processes, dependencies, and decisions.

Practical knowledge.
Public dates, in-house sessions, webinars — tailored to your specific requirements.
 AI-generated
Digital Sovereignty – Add-on to QMS Development
Digital Sovereignty and Quality Management Systems A certified quality management system offers numerous advantages. The consistent focus is on unlocking…

Cyber Resilience Act (CRA) – Product Readiness Check
Short description: Evaluation of your products with digital elements with regard to CRA requirements. Service description The Cyber Resilience Act…
NIS2 – Applicability & Gap Analysis
Short description: Analysis of your applicability and implementation readiness regarding NIS2. Service description The NIS2 Directive expands the requirements…
Common inquiries from our clients.
How does a collaboration proceed?
We always begin with a non-binding initial consultation to understand your requirements. This is followed by a concrete proposal — fully transparent, without hidden costs.
Do you offer in-house training courses?
Yes. All training courses can be booked as open-enrollment sessions or conducted in-house — tailored to your specific organization upon request.
In which languages do you deliver training?
Standard delivery is in German and English. Additional languages are available upon request.
Ready for your next step?
Speak with us about your challenges — non-binding, direct, concrete.